A new Windows malware strain called VOLTA-AUTODOXER does more than grab passwords. After it empties a computer of credentials, cookies and wallets, it hands the loot to a large language model and asks the AI to work out how much the victim is worth. Cisco Talos uncovered the malware through CAIRN, its research program that tracks attack tools with built-in AI features.
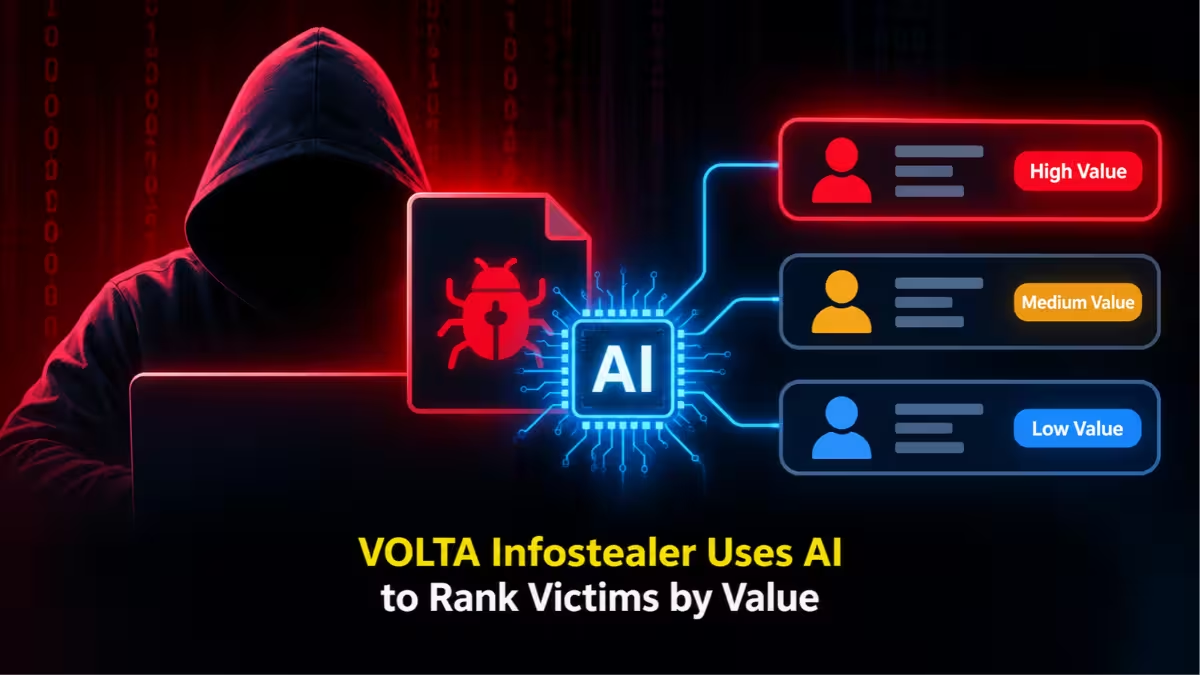
Security teams have watched criminals use AI to write phishing emails and code. VOLTA shows a different shift. Here, the AI acts as the attacker's analyst, sorting through stolen data so the criminal can jump straight to the most profitable targets.
What Is the VOLTA Infostealer and Why Does It Matter?
VOLTA (the name the malware gives itself internally) is an infostealer that targets Windows PCs. It deletes itself after it runs, which makes cleanup and forensic analysis harder. Researchers describe the stealing component as mature and well built. The AI layer sits on top as an optional extra, so the malware still works as a normal stealer when no AI key is configured.
Talos has not linked VOLTA to a specific group, and it has not shared victim numbers. The researchers also did not confirm how widely criminals use it in the wild.
What Information Does VOLTA Steal From Windows PCs?
VOLTA casts a very wide net. On an infected machine, it targets:
- Saved passwords, cookies and payment cards from Chromium browsers, plus Firefox data
- Outlook and Thunderbird email profiles and Slack workspaces
- Discord, Telegram, Steam, Battle.net and Roblox sessions
- Microsoft OAuth tokens
- SSH keys and cloud provider configuration files
- Every saved Wi-Fi password, dumped in plain text
- Cryptocurrency wallet seed phrases and wallet vaults
- Screenshots of the desktop
The wallet theft goes a step further than most stealers. VOLTA runs a built-in cracker against encrypted wallet vaults on the spot instead of just copying the files.
To pull session tokens out of Chrome, VOLTA bypasses App-Bound Encryption by quietly launching the browser in headless mode, with no visible window.
How Does VOLTA Turn Gmail Receipts Into a Victim's Home Address?
Raw credentials only tell part of the story. VOLTA uses the sessions it just stole to dig deeper into the victim's life.
It logs into the victim's Gmail with the stolen tokens and hunts for order receipts from Amazon, Walmart, PayPal, DoorDash, Uber Eats and Grubhub. Those receipts confirm a home address. It also pulls order history straight from Uber Eats and DoorDash, reuses the Discord token to fill in the user's profile, and checks the market value of Roblox items through a live Rolimons lookup.
All of this goes into what the malware treats as an evidence file on the person. It holds their location and home address, employer and work domain, a guessed birth year, the last four digits of their cards, Slack workspaces, document author metadata, signs of iPhone backups and a Roblox account valuation.
The focus on Roblox, Discord and gaming accounts suggests the author has younger, highly online users in mind, alongside office workers whose cloud keys and Microsoft tokens open doors into companies.
How Does VOLTA Use Claude, Kimi and Gemini to Score Victims?
VOLTA saves the collected profile locally as a text report, converts it to JSON and sends it to OpenRouter, a service that routes requests to many AI providers through one API. The request travels over the victim's own internet connection.
The malware's settings point to these models:
| Setting | Value |
|---|---|
| Gateway | OpenRouter chat completions API |
| First choice | Anthropic Claude Opus 4.6 |
| Backup 1 | Moonshot AI Kimi K2 |
| Backup 2 | Google Gemini 2.5 Flash |
| Temperature | 0.2 (low randomness, consistent replies) |
A roughly 240-word system prompt tells the model to play a forensic intelligence analyst writing a target assessment. It forbids the model from adding outside knowledge and limits it to the stolen data. The prompt asks for a summary of the person, a section that ranks their valuables by how easily they convert to cash (low, medium or high), and a section that grades their security habits and password hygiene.
The prompt also pushes the AI to connect dots a human might miss. For example, it asks the model to check whether a Wi-Fi password matches the victim's surname, or whether passwords borrow from their name, address or university.
The AI reply comes back as an analysis file. VOLTA zips it with the identity report and ships both out.
Why VOLTA Switches to Another AI Model When One Refuses
The author clearly expected AI safety filters to push back. VOLTA scans each reply for refusal phrases such as "I can't" or "I'm not able," and it also flags replies that look too thin. When it detects a refusal, it moves down the chain to the next model. If all three fail, or if the buyer never added an API key, VOLTA skips the AI step and sends the raw data anyway.
The prompt itself avoids openly criminal wording, which makes it harder for model safeguards to spot the intent. This refusal-proof design may become standard in future AI-enabled malware.
How VOLTA Sends Stolen Data Out Through Telegram
VOLTA sends stolen data to the attacker through a Telegram channel at three points:
- Right after the theft, with passwords, cookies, cards, wallets, game tokens, Wi-Fi keys and screenshots
- After the AI analysis, with the profile and the model's assessment
- After the enrichment step, with Gmail receipts and food delivery history
Because every endpoint belongs to third parties like Telegram and OpenRouter, the attacker runs no servers of their own. That leaves defenders with fewer infrastructure targets to take down.
Is VOLTA Sold as a Malware Kit?
VOLTA ships with a template that has six fill-in slots for the Telegram channel, API keys and other settings. A builder fills those slots and compiles a fresh binary for each buyer. This strongly points to a malware-as-a-service model.
The slot values look encrypted, but the key comes from constants inside the same file, so anyone who reverses the sample can recover them. The weak encryption seems designed to reassure buyers rather than protect anything.
The bigger worry is access. A buyer with no skills can point VOLTA at victims and receive ranked, ready-to-use target reports in a Telegram inbox. The AI removes the slow, manual work of reading through stolen logs, and faster triage means criminals can use tokens and passwords before victims change them.
How VOLTA Compares With Other AI-Powered Malware Like NIK C2
Criminals now add AI to attack tools at a steady pace. Talos recently flagged NIK C2, a Go-based remote access tool for Windows that supports more than 50 commands. When its operator supplies no OpenAI key, NIK C2 searches the victim's environment variables for one and uses it, so the victim pays for the attack on their own data. Researchers call this kind of stolen AI access LLMjacking. Another implant reported earlier lets a panel of several LLMs vote on its next move.
How to Protect Your PC and Accounts From VOLTA
For home users:
- Download software only from official sources. Infostealers often hide in cracked apps, game cheats and fake installers.
- Use a password manager instead of saving passwords in the browser.
- Turn on passkeys or hardware security keys for important accounts.
- Never store wallet seed phrases as plain text files on your PC.
For IT and security teams:
- Block or alert on Chrome launching with the headless flag from any process outside known developer tools. This cuts off VOLTA's main route to Chrome sessions.
- Watch for unexpected outbound traffic to OpenRouter and other AI APIs from regular workstations.
- Deploy EDR and stop programs from running out of Downloads, Temp and AppData folders.
- Require phishing-resistant MFA for privileged accounts.
What to Do If You Think VOLTA Infected Your Computer
- Look for a file named volta_debug.txt inside your AppData folder and keep it. The main program may have deleted itself, but this log lists exactly what it stole and whether the AI step worked.
- Sign out of all active sessions and revoke refresh tokens, since stolen cookies let attackers skip your password.
- Change every password stored in the browser and rotate all API keys, SSH keys and cloud credentials.
- Move any crypto stored with a plain text seed phrase to a brand new wallet, ideally with a seed generated on an offline device.
- Organizations should review sign-in logs, OAuth app grants and mailbox rules for signs of misuse.
Why VOLTA Signals a Bigger Shift in Cybercrime
VOLTA does not invent a new way to steal data. Its danger lies in what happens next. By handing the analysis to an AI model, it turns a messy pile of stolen files into a sorted list of who to hit first and how. As AI keeps lowering the skill needed to run these attacks, strong account security and careful download habits matter more than ever.
Frequently Asked Questions
What is the VOLTA infostealer?
VOLTA, which calls itself VOLTA-AUTODOXER, is a Windows infostealer that steals passwords, cookies, wallets and sessions, then asks an AI model to rank the victim's data by how much money it could bring. The malware deletes itself after it runs.
Which AI models does VOLTA use?
VOLTA sends its requests through OpenRouter. It tries Anthropic's Claude Opus 4.6 first, then Moonshot AI's Kimi K2, then Google's Gemini 2.5 Flash. If a model refuses or gives a weak reply, the malware moves to the next one.
Can VOLTA work without AI?
Yes. The AI stage is an optional add-on. If the buyer does not add an API key, VOLTA still steals the data and sends it out through Telegram.
How do I know if VOLTA infected my PC?
Check your AppData folder for a file named volta_debug.txt. The malware writes a log there that shows what it collected and whether the AI step worked. The main program may delete itself, so keep this file if you find it.
What should I do if VOLTA stole my data?
Sign out of all active sessions, revoke tokens, and change every password saved in your browser. Rotate any API keys, SSH keys and cloud credentials. Move crypto to a new wallet if your seed phrase sat in a plain text file.